Homelab
A NixOS + k3s homelab where hosts, network, firewall, and cluster state are declared in Git and deployed only from CI.
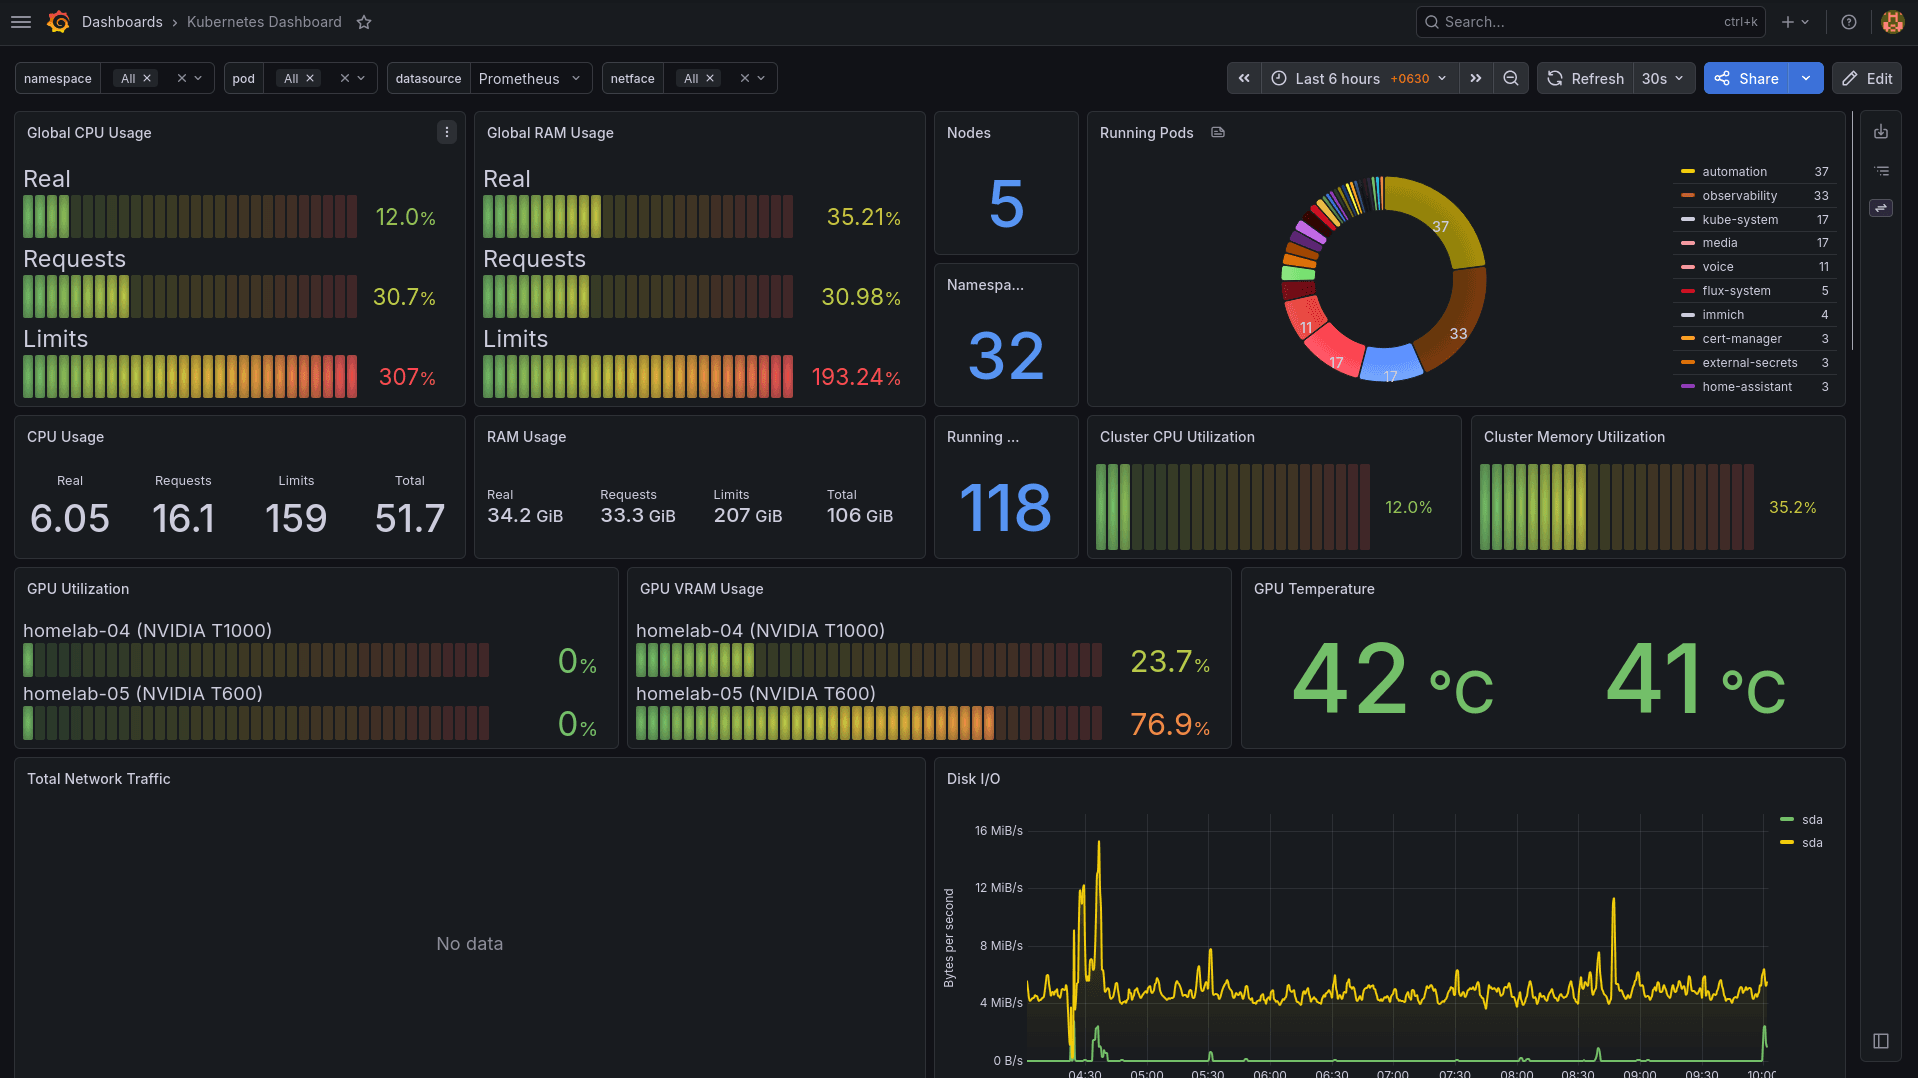
Overview
This is a greenfield rebuild of my homelab where the repository itself is the single source of truth for hosts, network, firewall, Kubernetes, secrets, and recovery. Seven NixOS hosts plus an OPNsense router are declared with flakes, disko, impermanence, and sops-nix, giving every machine a reproducible, encrypted, ephemeral root with no hand-edited state. First install goes through nixos-anywhere; subsequent activations use deploy-rs from NAS-hosted GitLab runners under a strict no laptop applies policy: infrastructure only ever changes from protected CI pipelines.
The cluster is k3s with Cilium as an eBPF kube-proxy replacement, peering to OPNsense over BGP for LoadBalancer IPAM across six VLANs. Flux reconciles ordered dependency layers with health checks and prune, while a local Zot registry serves digest-pinned images so workloads never pull straight from public registries. Zero trust holds throughout: public ingress goes only through Cloudflare Tunnels, admin access through a NetBird WireGuard mesh, and firewall state is managed by OpenTofu plus a custom typed Python OPNsense reconciler with encrypted pre-change backups and read-after-write verification. On top of that sits a ZFS NAS, source-first Home Assistant, a fully local voice assistant, Grafana/Loki observability, and isolated multiuser agent workspaces.
Highlights
- Built a declarative NixOS fleet with flakes, disko, impermanence, and sops-nix encrypted secrets.
- Enforced CI-only deployment with nixos-anywhere installs and deploy-rs activations, never from a laptop.
- Peered k3s to OPNsense over BGP with Cilium kube-proxy replacement and LoadBalancer IPAM across six VLANs.
- Reconciled cluster state with Flux ordered dependency layers, health checks, and prune.
- Isolated the supply chain behind a local Zot registry with digest-pinned workloads.
- Wrote a typed Python OPNsense reconciler with encrypted pre-change backups and read-after-write verification.
- Held zero trust with Cloudflare Tunnels, NetBird, cert-manager, and SOPS/age, with no exposed admin ports.
- Ran a ZFS NAS, GitLab CI runners, Grafana/Loki observability, and source-first Home Assistant on the same fleet.
Links
Stack
NixOS / k3s / Flux / Cilium / OpenTofu / OPNsense / Cloudflare / NetBird / Grafana / Home Assistant / GitLab CI / ZFS / sops-nix / Python